Pillar 03 · Cybersecurity

Find the flaws, then fix them: the same team.

Sooatek audits the security of your web and mobile applications and their technical GDPR compliance, fixes what it finds and hardens your servers. The team that audits is the team that writes the code: no report left hanging.

OWASP ASVS · CVSS · no active test without written authorization

Requests flagged “urgent” (email subject, or the “PHP2Shell emergency” topic in the form) go to the top of our inbox. Do not send passwords or exploitable details by email.

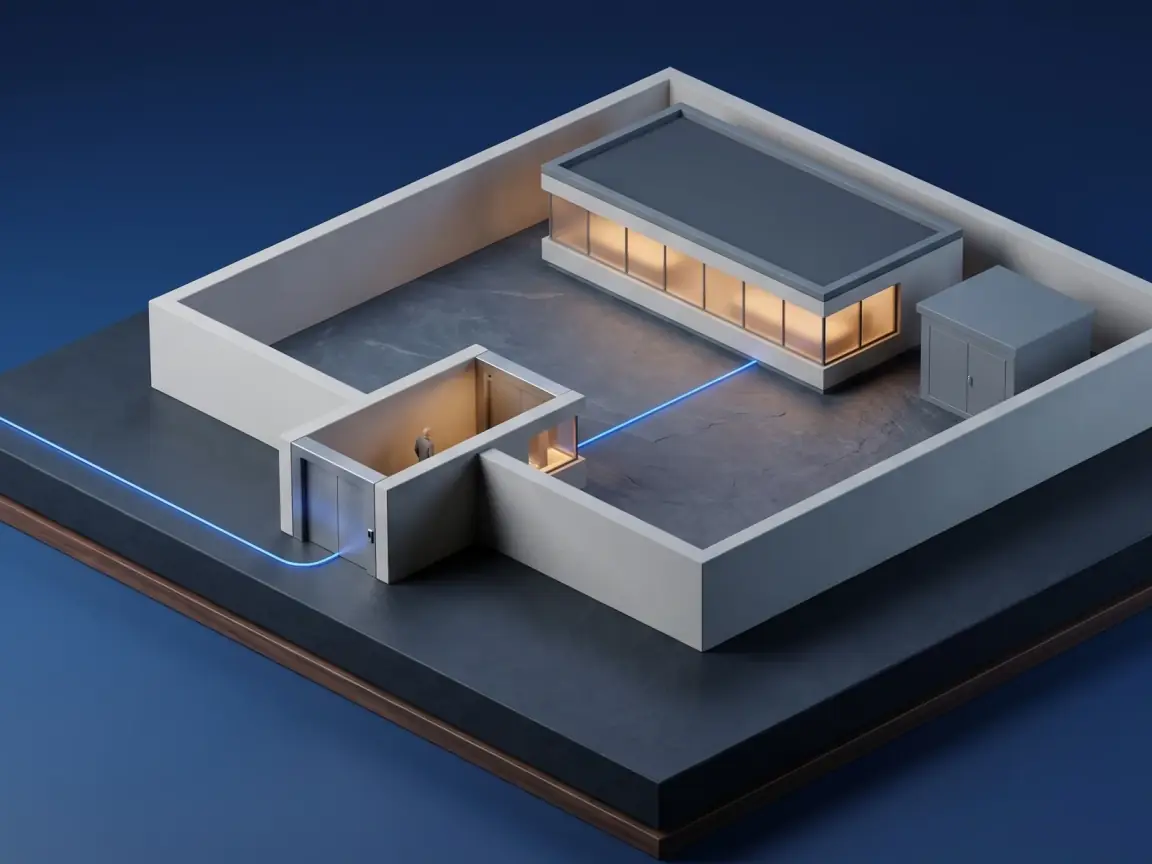
Illustration: a model enclosure on a slate base; you enter through a guarded airlock with two doors, which opens onto a courtyard and a lit building.
FIG. 01 — A single, controlled entrance · 3D illustration

§ 01 / What we do

Find, fix, respond, prevent.

Four areas, from the first audit to emergency response, on applications that are already live.

  1. Application and GDPR audit

    Code and configuration review, OWASP ASVS, exposed secrets and dependencies, access control, the technical side of GDPR (Article 32). Score out of 100, Go/No-Go verdict.

  2. Remediation and hardening

    What the audit found, or what a third party reported to you: fixed, then re-tested. Two-factor authentication, access review, headers, TLS, email (SPF, DKIM, DMARC).

  3. Emergency

    Critical security advisory or reported vulnerability: verified backup, mitigation in place, fix applied, external check, written report.

  4. Prevention

    Monthly vulnerability monitoring with human triage, security checks in your continuous integration, upgrades before end of support.

§ 02 / Offers

Two fixed-price offers, on quote.

Start with the audit, or go straight to remediation if a report already exists (ours or a third party’s). The express audit covers a brochure site or a simple application, in 2 days. Up to 3 times cheaper than the European market, for the same standards.

Offer 09

5 days

Security and GDPR audit

A score out of 100, ranked vulnerabilities, a clear verdict and a remediation plan, from a team that knows how to fix.

Included

  • Score out of 100 and Go/No-Go verdict
  • Vulnerabilities ranked by CVSS / OWASP ASVS
  • Exposed secrets and dependencies
  • 45-minute debrief

Pricing

Fixed price, on quote
Offer 10

1 to 2 weeks

Security hardening and NIS2 readiness

Vulnerabilities fixed, foundations hardened, monitoring in place, and a plan to prepare for NIS2.

Included

  • Priority vulnerabilities fixed and re-tested
  • Hardening: two-factor authentication, access, TLS, email
  • Or a hygiene review and NIS2 action plan
  • Optional vulnerability monitoring

Pricing

Fixed price, on quote

Agencies and IT services companies: −20% off the direct rate, white label. The agency program

Compare all offers

§ 03 / Method

A written method, the same for every audit.

Method

An 8-phase method, followed in the same order for every audit. A human review validates each finding before the report.

Output Score out of 100 · Go/No-Go verdict

Then

  • Each finding carries a score, a reference and a fix.
  • A matrix ranks the fixes by urgency and effort.
  • Automated checks keep the vulnerabilities from coming back.

§ 04 / Frameworks and tools

Public frameworks, automated checks.

Findings rely on recognized grids; automated checks complement human review, they do not replace it.

Frameworks

  • OWASP Top 10
  • OWASP ASVS
  • PTES
  • CVSS 3.1
  • CWE
  • GDPR

Vulnerabilities are ranked by CVSS and OWASP.

Automated checks

  • Static analysis

    The code is scanned for dangerous patterns.

    Tool: Semgrep

  • Secret detection

    Keys and passwords, all the way into the Git history.

    Tool: Gitleaks

  • Dependency analysis

    The libraries in use, compared with known vulnerabilities.

    Tool: Trivy

Research and development We equip our audits with sandboxed AI agents running on local models: only the declared scope can be reached, and a human validates each finding.

§ 05 / What you receive

A deliverable for each reader.

Management decides, developers fix: each gets the document they need.

  1. A report for management, free of jargon: risks as concrete scenarios and the action plan.
  2. A technical report for your developers: each vulnerability with its proof, its score and its fix.
  3. A matrix that ranks the fixes by urgency and effort, with their price.
  4. A security checklist to add to your deployment pipeline.
  5. After an emergency: an intervention report: what was done, what was checked, what changes for your users, how to roll back.

§ 06 / What we find

What we find most often when we open old PHP code.

Typical findings, with no numbers and no names: none is tied to a client.

  1. A web shell already on the server, planted long before the audit.

  2. An unauthenticated file upload that leads to code execution.

  3. A back office reachable without authentication.

  4. SQL injections in hand-built queries.

  5. Database administration tools exposed to the internet.

  6. Plain-text secrets in the Git repository, all the way into the history.

  7. Sensitive data stored in the web root.

  8. PHP or framework versions that no longer receive fixes.

The real work is finding them all, fixing them, then keeping them from coming back.

§ 07 / Interventions

What we have secured.

Anonymized clients, no exploitable detail.

  • Intervention 01

    Anonymized

    Recruitment website of a large group

    • Remediation
    • Upgrade
    Context
    Security scans run by the client’s team had reported vulnerabilities.
    Action
    Site upgrade and remediation of the reported issues, in pre-production.
    Verification
    A new scan by the client, then a production release with a written rollback procedure.

    Outcome

    The client’s new scan found no exploitation path.

  • Intervention 02

    Anonymized

    Information system of a sports federation

    • Audit
    • Remediation
    • Two-factor authentication
    Context
    Five connected applications: management, mobile, members’ portal, competitions, payment.
    Action
    Eight-phase audit, code review and testing in pre-production, two reports and a priority matrix.
    Verification
    Fixes carried out according to the plan; automated checks proposed and a best-practice guide for users.

    Outcome

    Priority findings handled; adaptive two-factor authentication in production.

§ 08 / NIS2 and hygiene

Prepare for NIS2 without waiting for the law.

The French transposition of the NIS2 directive is not final as of 26 October 2026. Part of the work does not depend on the final text: that is the part we do with you.

  • Two-factor authentication on sensitive access
  • Review of accounts and permissions
  • Backups and restore procedure reviewed
  • Inventory of applications, servers and versions
  • Email protected against spoofing (SPF, DKIM, DMARC)
  • A costed action plan, prioritized by risk

Before us, or alongside us

  • MonAideCyber (ANSSI)

    A free maturity assessment run by a volunteer helper, in France: our technical audit complements it, it does not replace it.

  • Cybermalveillance.gouv.fr

    If an attack is under way, start there; we then restore your applications.

What we do not do

  • PASSI-qualified penetration testing.
  • Internal infrastructure or directory (Active Directory) audits.
  • 24/7 incident response and digital forensics.
  • The data protection officer (DPO) role.
  • A “guaranteed NIS2 compliance”.

§ 09 / Questions

Frequently asked questions.

How much does a security audit cost?

The security and GDPR audit is a 5-day fixed-price engagement, priced before we start. The remediation plan is costed in the report.

Do you fix what the audit finds?

Yes: that is the difference from an audit firm. The same team fixes, re-tests and sets up automated checks. Your team can also do it with our report.

Do you test production?

No. Active tests take place in pre-production, with written authorization. In production, we observe without attacking.

Do you run penetration tests?

We do not sell qualified (PASSI) penetration testing. Our audit is a technical review of the code and configuration, with targeted active tests in pre-production, followed by the fixes.

Is my company covered by NIS2?

It depends on your size and sector, and the French transposition law is not final as of 26 October 2026. The hygiene measures (two-factor authentication, access review, backups, inventory) can be prepared now.

My application runs on a version that is no longer maintained.

We first put the possible protections in place, then we migrate at a fixed price.

A reported vulnerability, a critical advisory, an audit to prepare?

Describe your application in a few lines. Requests flagged “urgent” (email subject, or the “PHP2Shell emergency” topic in the form) go to the top of our inbox. Do not send passwords or exploitable details by email.